Seventy three percent of marketers say they plan to let AI agents access unified customer profiles within the next year, according to recent eMarketer survey data. Almost none of them have rewritten their identity resolution vendor contracts to account for it. If your agency or brand is still running on a data processing agreement drafted before generative AI existed, you are one subpoena away from finding out how thin that paper really is.
Identity resolution vendor contracts used to be boring. You signed, you got a unified customer ID, you moved on. That era is over. Now those same vendors are plugging AI agents directly into the resolved identity graph, letting algorithms make real time decisions about who a customer is, what they are worth, and what message to serve them next. The contract you signed for a database now governs an autonomous decision engine. Most legal teams have not caught up.
Why the Old Data Processing Agreement No Longer Covers You
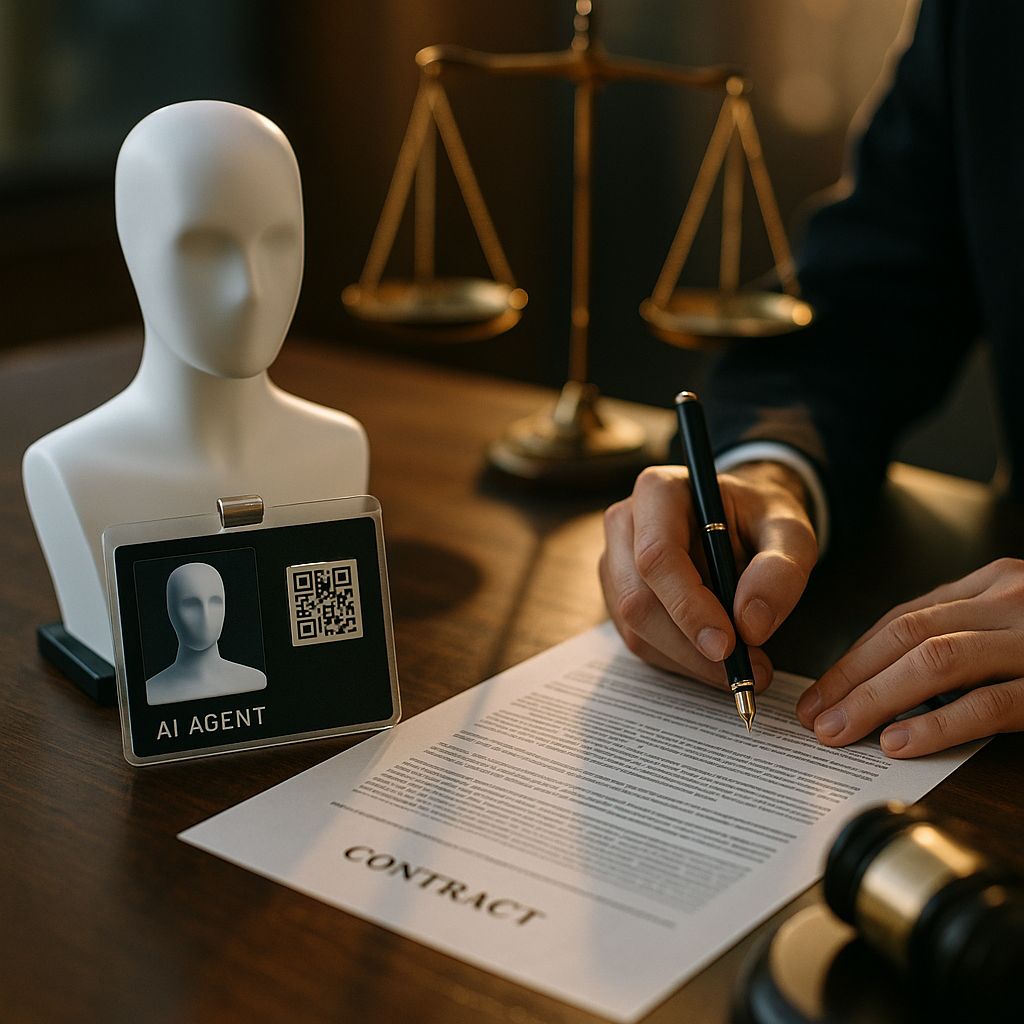
A standard identity resolution agreement typically covers three things: data ingestion, matching logic, and output format. It says nothing about model training, agent autonomy, or downstream decisioning. When a vendor like a CDP or identity graph provider starts feeding resolved profiles into an AI agent that personalizes offers, drafts outreach, or triggers automated bids, you have introduced a new risk surface the original contract never anticipated.
Think about what actually changed. Identity resolution used to be a static lookup: match this email to that device ID, append a household score, done. Now the matched profile becomes training data, or worse, live input for a model making decisions in real time. If that model hallucinates a segment, misclassifies a protected category, or leaks a profile through a prompt injection, your original contract’s liability clauses were written for a world where none of that was possible.
If your identity resolution vendor contract does not name the specific AI agent, its training data boundaries, and who owns the output, you are indemnifying a process you cannot audit.
This is not theoretical. Our sister coverage on CDP identity resolution has already flagged how purpose limitation clauses break down the moment a vendor repurposes matched data for a use case nobody consented to. AI agents accelerate that problem because they generate new uses on the fly, not just the ones a product manager wrote into a spec document.
What to Demand Before You Sign Anything
Here is the uncomfortable truth: most vendors will not volunteer these terms. You have to ask, in writing, and you have to walk if they stonewall. These are the non-negotiables.
- Named agent disclosure. The contract must name every AI agent, model, or automated system that touches resolved identity data, not a vague reference to “machine learning capabilities.” If the vendor cannot tell you which model ingests your customer graph, they do not control their own supply chain, and neither do you.
- Training data exclusion clause. Explicitly prohibit your resolved identity data from being used to train or fine-tune any model that is not exclusively serving your account. This is the single most common gap found during vendor audits.
- Audit rights with teeth. You need the contractual right to request logs showing what the agent did with a given customer record, not just assurances. Quarterly access to decisioning logs should be standard, not a premium add-on.
- Kill switch provisions. If the agent misbehaves (discriminatory outputs, data leakage, a regulatory complaint), you need the unilateral right to suspend agent access to your data within a defined window, typically 24 to 48 hours, without breach penalties.
- Output ownership clarity. Who owns the decisions the agent makes using your data? If the agent generates a lookalike segment or a propensity score, that output is derivative of your customer data and should be contractually yours, not a reusable asset the vendor sells to other clients.
- Subprocessor transparency. Many identity resolution vendors route data through third party LLM providers for enrichment or scoring. You need a full subprocessor list, updated in real time, not buried in an annual compliance report.
None of this is exotic. It is the same discipline brands already apply to platform data sharing agreements, just extended to cover the agentic layer that identity vendors have quietly bolted on.
The Liability Question Nobody Wants to Answer
Ask any identity resolution vendor who is liable if their AI agent misuses resolved data in a way that triggers an FTC complaint or a state privacy action. Watch how fast the conversation shifts to “shared responsibility” language. That phrase is doing a lot of work to avoid committing to anything specific.
Shared responsibility is fine, as long as the contract defines exactly where your responsibility ends and theirs begins. In practice, most vendor paper puts the brand on the hook for consent collection and the vendor on the hook for processing, but AI agents blur that line because the agent is often the one deciding what counts as a permissible use in the moment. Our breakdown of the SECURE Data Act patchwork covers how state level enforcement is already testing exactly this kind of ambiguity, and regulators are not inclined to split hairs in your favor.
Push for indemnification language specific to autonomous decisioning, not generic data breach boilerplate. If the vendor’s standard contract only indemnifies for “unauthorized access” and not for “autonomous misuse of authorized access,” you have a gap big enough to drive a class action through.
Consent Chains Get Longer, Not Shorter
Every time an AI agent touches a resolved identity, it adds a link to the consent chain. The customer agreed to let your brand use their email. Did they agree to let an AI agent cross reference that email against a device graph to build a probabilistic household score, then use that score to decide ad frequency in real time? Probably not explicitly, and that is the exposure.
This is where the work connects directly to consent architecture covered in our piece on unified customer profiles. The consent gap identified there gets wider, not narrower, once an autonomous agent is making the matching decisions instead of a documented, static rule set. A human engineer writing match logic can be audited by reading code. An AI agent making probabilistic matches in real time is harder to pin down after the fact, which is exactly why your contract needs to require decision logging as a baseline, not a nice to have.
A resolved identity touched by an undisclosed AI agent is not a technical footnote. It is a consent violation waiting for a regulator to notice.
Some brands are responding by building parallel identity graphs tied to creator and influencer content specifically, since that data often carries different consent provenance than first party ecommerce data. The analysis in creator identity graphs is worth reading alongside this piece, because the regulatory blind spot there mirrors the one forming around AI agents touching broader customer identity data.
Negotiation Tactics That Actually Move the Needle
Legal teams often approach vendor negotiations as a checklist exercise. That does not work with AI agent clauses because most vendors have not built the internal infrastructure to honor granular requests yet. Here is what works in practice.
- Ask for a technical walkthrough, not just redlines. Have your data team sit in on a call where the vendor’s engineers explain exactly how the agent accesses resolved profiles. If they cannot produce an engineer who can answer this in plain language, that is a signal.
- Request a sandboxed pilot before full integration. Limit agent access to a non-production dataset for 30 to 60 days while you validate logging, audit access, and kill switch functionality actually work as written.
- Tie payment milestones to compliance proof. Do not release full contract value until the vendor demonstrates, in writing, that subprocessor disclosures and audit logs are functioning.
- Build in a renegotiation trigger. Require the contract to reopen automatically if the vendor changes the underlying AI model or adds a new subprocessor. Static contracts cannot govern a vendor stack that updates models quarterly.
This mirrors the approach outlined in our coverage of AI negotiated creator contracts, where insurance and liability terms had to be rebuilt from scratch once AI entered the negotiation itself rather than just the execution.
What Happens When You Skip This Step
Brands that feed customer data into agentic systems without updated contracts are discovering the hard way that “the vendor’s AI did it” is not a defense regulators or plaintiffs’ attorneys accept. The FTC has made clear in recent guidance that accountability follows the data, not the tool. If your brand collected the original consent, you likely retain liability regardless of how many AI layers sit between collection and activation.
The UK’s Information Commissioner’s Office has taken a similarly firm stance on automated decisioning, requiring explainability that most off the shelf AI agents simply cannot provide today. If your identity resolution vendor operates across US and UK customer bases, that gap alone should be enough to pause any contract renewal until agent transparency terms are nailed down.
Take the next vendor renewal as your checkpoint. Do not renew an identity resolution contract until legal, security, and marketing have jointly reviewed agent disclosure, training data exclusions, and kill switch terms, because the cost of fixing this after a breach is always higher than the cost of negotiating it now.
Frequently Asked Questions
What is identity resolution in the context of AI agents?
Identity resolution is the process of matching fragmented customer data points (emails, device IDs, purchase history) into a single unified profile. When AI agents are layered on top, they use that unified profile to make autonomous decisions like personalization, scoring, or outreach, which introduces new contractual and compliance risk beyond standard data matching.
Why do existing data processing agreements fail to cover AI agents?
Most data processing agreements were written to cover static matching and storage, not autonomous decisioning. They rarely name specific AI models, define training data boundaries, or include audit rights for agent behavior, leaving brands exposed when a vendor adds agentic capabilities without renegotiating terms.
What specific clauses should a brand demand from an identity resolution vendor?
At minimum, demand named agent disclosure, a training data exclusion clause, audit rights with log access, kill switch provisions allowing rapid suspension, clear output ownership, and full subprocessor transparency updated in real time.
Who is liable if an AI agent misuses resolved customer data?
Liability typically remains with the brand that collected original consent, even if a third party vendor’s AI agent performed the misuse. Regulators including the FTC have signaled that accountability follows the data, not the tool, making specific indemnification language for autonomous decisioning essential.
How often should identity resolution vendor contracts be reviewed?
At minimum, every renewal cycle, but ideally any time the vendor changes its underlying AI model or adds a new subprocessor. Building an automatic renegotiation trigger into the contract is more reliable than relying on annual review calendars.
Top Influencer Marketing Agencies
The leading agencies shaping influencer marketing in 2026
Agencies ranked by campaign performance, client diversity, platform expertise, proven ROI, industry recognition, and client satisfaction. Assessed through verified case studies, reviews, and industry consultations.
Moburst
-
2
The Shelf
Boutique Beauty & Lifestyle Influencer AgencyA data-driven boutique agency specializing exclusively in beauty, wellness, and lifestyle influencer campaigns on Instagram and TikTok. Best for brands already focused on the beauty/personal care space that need curated, aesthetic-driven content.Clients: Pepsi, The Honest Company, Hims, Elf Cosmetics, Pure LeafVisit The Shelf → -
3
Audiencly
Niche Gaming & Esports Influencer AgencyA specialized agency focused exclusively on gaming and esports creators on YouTube, Twitch, and TikTok. Ideal if your campaign is 100% gaming-focused — from game launches to hardware and esports events.Clients: Epic Games, NordVPN, Ubisoft, Wargaming, Tencent GamesVisit Audiencly → -
4
Viral Nation
Global Influencer Marketing & Talent AgencyA dual talent management and marketing agency with proprietary brand safety tools and a global creator network spanning nano-influencers to celebrities across all major platforms.Clients: Meta, Activision Blizzard, Energizer, Aston Martin, WalmartVisit Viral Nation → -
5
The Influencer Marketing Factory
TikTok, Instagram & YouTube CampaignsA full-service agency with strong TikTok expertise, offering end-to-end campaign management from influencer discovery through performance reporting with a focus on platform-native content.Clients: Google, Snapchat, Universal Music, Bumble, YelpVisit TIMF → -
6
NeoReach
Enterprise Analytics & Influencer CampaignsAn enterprise-focused agency combining managed campaigns with a powerful self-service data platform for influencer search, audience analytics, and attribution modeling.Clients: Amazon, Airbnb, Netflix, Honda, The New York TimesVisit NeoReach → -
7
Ubiquitous
Creator-First Marketing PlatformA tech-driven platform combining self-service tools with managed campaign options, emphasizing speed and scalability for brands managing multiple influencer relationships.Clients: Lyft, Disney, Target, American Eagle, NetflixVisit Ubiquitous → -
8
Obviously
Scalable Enterprise Influencer CampaignsA tech-enabled agency built for high-volume campaigns, coordinating hundreds of creators simultaneously with end-to-end logistics, content rights management, and product seeding.Clients: Google, Ulta Beauty, Converse, AmazonVisit Obviously →