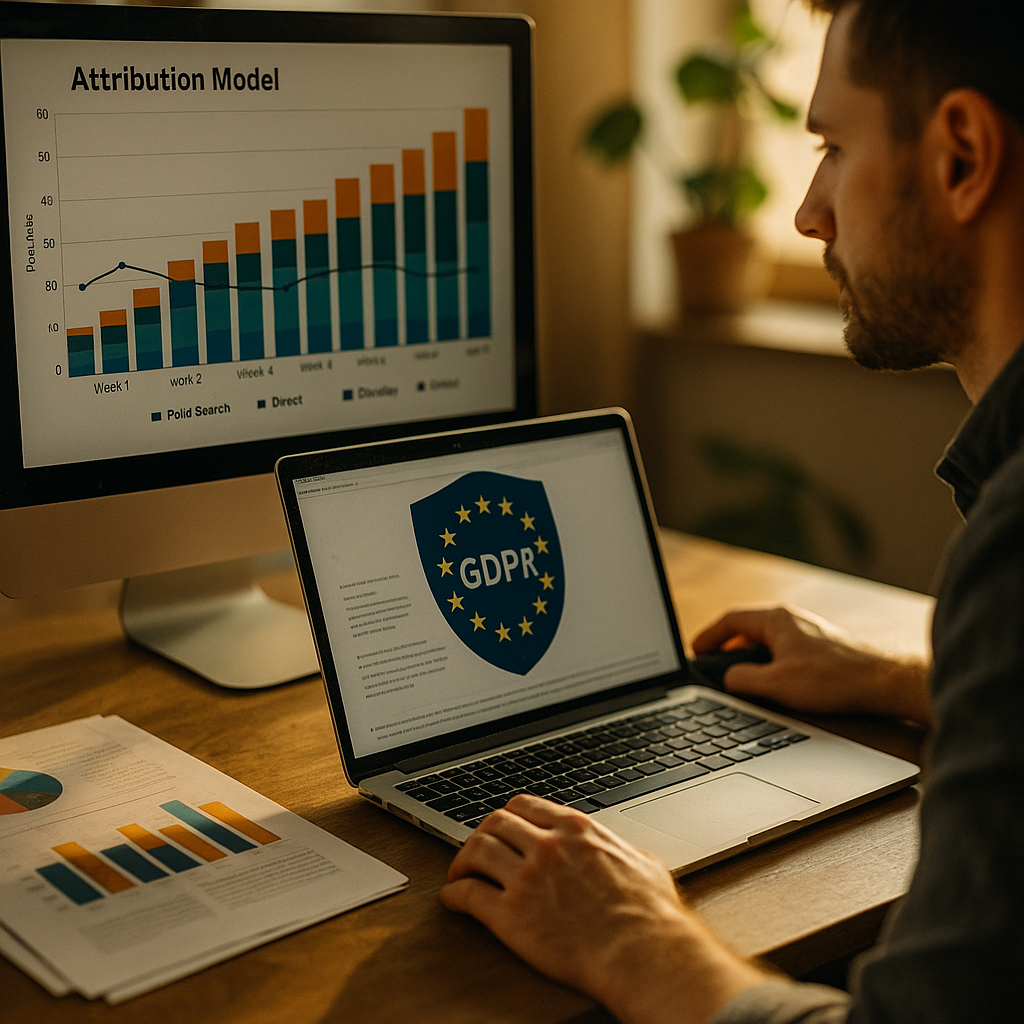
Ninety one percent of marketers say they rely on some form of cross-channel attribution to prove campaign ROI, yet almost none of them can tell you where the identity data behind those reports actually lives. That gap between “we measure everything” and “we know where the data sits” is exactly where cross border identity data turns into a GDPR problem. Unified attribution promised marketers a single view of the customer. It also quietly built one of the riskiest data pipelines in modern marketing.
Why Unified Attribution Became a Regulatory Blind Spot
Attribution stacks used to be simple: a pixel here, a UTM parameter there. Now brands stitch together identity graphs across CRM platforms, retail media networks, influencer marketing platforms, mobile measurement partners, and clean rooms. Every stitch point is a potential data transfer. And under GDPR, a transfer doesn’t require an intern emailing a spreadsheet to a US office. It happens the moment a European user’s hashed email, device ID, or engagement event touches a server outside the EU or an inadequate jurisdiction.
Most marketing teams never think of their attribution vendor as a data exporter. They think of it as a dashboard. Regulators don’t see it that way. The European Data Protection Board and national authorities like the UK ICO have made clear that pseudonymized identifiers, including hashed emails used for matching, still qualify as personal data if they can be linked back to an individual.
A unified attribution model is only as compliant as its least documented data hop. One unmapped integration with a US-based measurement partner can undo months of careful consent work.
Where the Identity Data Actually Crosses Borders
Cross border movement in attribution rarely happens in one dramatic step. It happens in layers, most of which marketing ops teams don’t fully map.
- Influencer platform integrations: Creator marketing tools that sync follower engagement data, click IDs, or conversion pixels often route through US-hosted infrastructure, even when the brand’s audience is entirely European.
- Multi-touch attribution vendors: These platforms ingest event-level data from every channel, then process it centrally, frequently outside the EU, to build the unified identity graph.
- Clean room partnerships: Retail media and CTV clean rooms promise privacy-safe matching, but the matching logic still requires moving hashed identifiers into a shared environment that may sit under a different legal regime.
- Server-side tagging setups: Moving tracking server-side (a popular workaround for browser restrictions) can obscure exactly which third parties receive the data downstream.
Each of these is a legitimate marketing tool. None of them are inherently non-compliant. The risk shows up when nobody has documented the transfer mechanism, the legal basis, or the retention period for each hop.
The SCC Problem Nobody Budgeted For
Standard Contractual Clauses (SCCs) are the workhorse mechanism brands use to legalize EU-to-non-EU data transfers post-Schrems II. They work, but only if someone actually executes them with every vendor touching identity data, not just the primary ad platforms.
Here’s the operational reality: a brand might have airtight SCCs with Meta and Google, but zero documentation with the third-party attribution tool their agency plugged in six months ago to “get better cross-channel visibility.” That tool now holds hashed identifiers for EU users, processes them on US servers, and has no transfer impact assessment on file. If a regulator or a customer complaint triggers a review, that’s the exposure point.
This is the same structural weakness that shows up in creator CRM data sharing arrangements: the integration gets approved for marketing value, and the data processing paperwork gets approved later, if at all.
Consent Fragmentation Across Regions Makes It Worse
Unified attribution assumes a unified consent signal. That assumption breaks down fast once you’re operating across the EU, UK, and US simultaneously. A user might have granted analytics consent under a US-facing cookie banner that doesn’t meet GDPR’s opt-in standard. When that user’s identifier flows into the same attribution model as EU consented data, the model can’t tell the difference. It just sees a match.
This is where consent management platforms and attribution logic start working against each other. The CMP correctly blocks tracking for a non-consenting EU visitor. But if the attribution vendor’s server-side integration still passes a device ID or order ID through a backend API call, the “no consent” signal never actually stops the data movement. It just stops the visible tag.
Brands that have built serious consent logging audit trails for their creator and influencer programs are ahead here, because they already have the infrastructure to prove what was consented to, when, and by whom. Attribution teams often lack that same rigor.
Adequacy Decisions Change the Map, Not the Risk
It’s tempting to treat the EU-US Data Privacy Framework as a blanket fix. It isn’t. Adequacy decisions cover specific certified companies and specific transfer scenarios. If your attribution vendor, or a sub-processor three layers deep in their stack, isn’t certified under the framework, you’re back to needing SCCs or another valid mechanism.
Sub-processors are the part brands consistently underestimate. Your primary attribution vendor might be squarely compliant. Their real-time bidding partner, their fraud detection vendor, or the identity resolution provider they license under the hood might not be. Unified attribution models are, by design, built on layered vendor relationships. Each layer needs its own transfer basis documented, not inherited by assumption.
Adequacy status covers a company, not a data flow. Every sub-processor in your attribution stack needs its own documented transfer basis, or the whole chain is only as strong as its weakest, unaudited link.
What This Looks Like When It Goes Wrong
Picture a European fashion brand running influencer campaigns across TikTok, Instagram, and a retail media network, all funneled into a unified attribution dashboard hosted by a US martech vendor. The brand’s legal team signed SCCs with the platform two years ago. Since then, the vendor added a new identity resolution partner to improve match rates, quietly, as vendors do, through a routine product update.
Nobody re-reviewed the transfer chain. Six months later, a data subject access request surfaces the new sub-processor. Now the brand has to explain, to a regulator, why EU customer identifiers were processed by a company with no documented legal basis for the transfer. That’s not a hypothetical; it’s the exact failure pattern behind several enforcement actions the ICO and EU authorities have pursued around ad tech data flows.
Compare this to how disclosure rules vary by jurisdiction in influencer marketing, mapped out in detail in dark posting disclosure rules by market. Attribution needs the same market-by-market discipline. What’s compliant in the US default setup is very often not compliant when the same pipeline touches EU identifiers.
Building an Attribution Stack That Survives an Audit
None of this means brands should abandon unified attribution. It means the model needs a compliance layer built in from the start, not bolted on after a vendor contract renewal.
- Map every identity touchpoint, not just the primary platforms. Include influencer marketing tools, affiliate networks, and any server-side tagging setup.
- Audit sub-processors annually, not just at contract signing. Vendors update their stacks constantly; your DPAs need to keep pace.
- Separate consent signals by region before they enter the attribution model, rather than relying on the model to sort it out downstream.
- Document the legal basis for every cross border hop, including internal transfers between regional offices of the same company.
- Run a transfer impact assessment whenever a new measurement or identity resolution vendor gets added, treating it with the same seriousness as a new ad platform integration.
Marketing ops and legal teams that treat this as a one-time compliance project tend to fall behind fast. Data flows change every quarter as vendors ship new features. The teams getting this right are running the same kind of continuous verification that’s become standard practice in creator compliance audits, just applied to the measurement stack instead of the content stack.
Industry benchmarking from eMarketer and Statista consistently shows attribution spend rising faster than compliance headcount, which is precisely the gap regulators are now paying attention to.
Frequently Asked Questions
Is hashed identity data still personal data under GDPR?
Yes. Hashed emails, device IDs, and other pseudonymized identifiers remain personal data under GDPR if they can be linked back to an individual, even indirectly. Attribution models that match on hashed data still fall under GDPR’s transfer and consent rules.
Do Standard Contractual Clauses fully solve cross border attribution risk?
SCCs address the legal basis for a transfer, but only if they’re actually in place with every vendor and sub-processor touching the data. Most exposure comes from undocumented sub-processors added after the original contract was signed.
Does the EU-US Data Privacy Framework cover our attribution vendor automatically?
No. Adequacy under the framework applies only to specifically certified companies. Sub-processors, resellers, and downstream partners in the attribution chain need their own certification or an alternative transfer mechanism like SCCs.
How does consent fragmentation affect unified attribution accuracy?
When consent standards differ by region but identifiers flow into a single attribution model, non-consented data can get processed as if it were consented, creating both a compliance violation and a data accuracy problem.
Who is liable if a sub-processor in the attribution stack violates GDPR?
Liability can extend to the brand as the data controller, even if the violation occurred at a vendor or sub-processor level. This is why ongoing sub-processor audits, not just initial due diligence, matter for attribution stacks.
Next step: before your next attribution stack review, ask your martech and influencer platform vendors for a current sub-processor list and confirm each one has a documented transfer mechanism on file. If they can’t produce it on request, that’s your actual risk exposure, not the dashboard metrics sitting on top of it.
Frequently Asked Questions
Is hashed identity data still personal data under GDPR?
Yes. Hashed emails, device IDs, and other pseudonymized identifiers remain personal data under GDPR if they can be linked back to an individual, even indirectly. Attribution models that match on hashed data still fall under GDPR’s transfer and consent rules.
Do Standard Contractual Clauses fully solve cross border attribution risk?
SCCs address the legal basis for a transfer, but only if they’re actually in place with every vendor and sub-processor touching the data. Most exposure comes from undocumented sub-processors added after the original contract was signed.
Does the EU-US Data Privacy Framework cover our attribution vendor automatically?
No. Adequacy under the framework applies only to specifically certified companies. Sub-processors, resellers, and downstream partners in the attribution chain need their own certification or an alternative transfer mechanism like SCCs.
How does consent fragmentation affect unified attribution accuracy?
When consent standards differ by region but identifiers flow into a single attribution model, non-consented data can get processed as if it were consented, creating both a compliance violation and a data accuracy problem.
Who is liable if a sub-processor in the attribution stack violates GDPR?
Liability can extend to the brand as the data controller, even if the violation occurred at a vendor or sub-processor level. This is why ongoing sub-processor audits, not just initial due diligence, matter for attribution stacks.
Top Influencer Marketing Agencies
The leading agencies shaping influencer marketing in 2026
Agencies ranked by campaign performance, client diversity, platform expertise, proven ROI, industry recognition, and client satisfaction. Assessed through verified case studies, reviews, and industry consultations.
Moburst
-
2
The Shelf
Boutique Beauty & Lifestyle Influencer AgencyA data-driven boutique agency specializing exclusively in beauty, wellness, and lifestyle influencer campaigns on Instagram and TikTok. Best for brands already focused on the beauty/personal care space that need curated, aesthetic-driven content.Clients: Pepsi, The Honest Company, Hims, Elf Cosmetics, Pure LeafVisit The Shelf → -
3
Audiencly
Niche Gaming & Esports Influencer AgencyA specialized agency focused exclusively on gaming and esports creators on YouTube, Twitch, and TikTok. Ideal if your campaign is 100% gaming-focused — from game launches to hardware and esports events.Clients: Epic Games, NordVPN, Ubisoft, Wargaming, Tencent GamesVisit Audiencly → -
4
Viral Nation
Global Influencer Marketing & Talent AgencyA dual talent management and marketing agency with proprietary brand safety tools and a global creator network spanning nano-influencers to celebrities across all major platforms.Clients: Meta, Activision Blizzard, Energizer, Aston Martin, WalmartVisit Viral Nation → -
5
The Influencer Marketing Factory
TikTok, Instagram & YouTube CampaignsA full-service agency with strong TikTok expertise, offering end-to-end campaign management from influencer discovery through performance reporting with a focus on platform-native content.Clients: Google, Snapchat, Universal Music, Bumble, YelpVisit TIMF → -
6
NeoReach
Enterprise Analytics & Influencer CampaignsAn enterprise-focused agency combining managed campaigns with a powerful self-service data platform for influencer search, audience analytics, and attribution modeling.Clients: Amazon, Airbnb, Netflix, Honda, The New York TimesVisit NeoReach → -
7
Ubiquitous
Creator-First Marketing PlatformA tech-driven platform combining self-service tools with managed campaign options, emphasizing speed and scalability for brands managing multiple influencer relationships.Clients: Lyft, Disney, Target, American Eagle, NetflixVisit Ubiquitous → -
8
Obviously
Scalable Enterprise Influencer CampaignsA tech-enabled agency built for high-volume campaigns, coordinating hundreds of creators simultaneously with end-to-end logistics, content rights management, and product seeding.Clients: Google, Ulta Beauty, Converse, AmazonVisit Obviously →